Step 1: Create the Hub Router VM
This step deploys the BYOL SSR VM from the Azure Marketplace as a Hub Router. The deployment template creates the VM, attaches it to the hub WAN and LAN subnets, installs SSR 7.1.4 and configures the node as a conductor-managed router automatically.
Requirements
The following infrastructure must exist in your Azure subscription before deploying the hub router:
-
The
SSR-VNetVNet with thessr-hub-wanandssr-hub-lansubnets already created. -
A Managed Identity assigned the following minimum read permissions:
Microsoft.Compute/virtualMachines/readMicrosoft.Network/virtualNetworks/readMicrosoft.Network/networkInterfaces/read -
The conductor's public IP address from the Azure Conductor Deployment Guide.
A dedicated management subnet is not required. Management traffic travels over the WAN forwarding interface using Management Traffic over Forwarding Interfaces. If an out-of-band management interface is not used, management traffic travels over the WAN forwarding interface using management over forwarding.
Recommended VM Sizes
| Azure VM Size | Max vNICs | vCPU Cores | Memory |
|---|---|---|---|
| Standard_F8s_v2 | 4 | 8 | 16 GB |
| Standard_F16s_v2 | 4 | 16 | 32 GB |
| Standard_F32s_v2 | 8 | 32 | 64 GB |
| Standard_D8s_v5 | 4 | 8 | 32 GB |
For guidance on sizing for larger deployments, see System Requirements.
What the Template Creates
When you deploy the hub router using the BYOL conductor-managed router template, Azure automatically creates:
- A VM using the BYOL Session Smart image from the Marketplace, running SSR software and a basic configuration.
- Two network interfaces: WAN/public (
ge-0-0) and LAN/private (ge-0-1). - A network security group associated with each interface.
- A unique public IP address assigned to the WAN interface.
The router template supports an additional dedicated management interface. This is not used in this guide; in this example, management traffic travels over the WAN forwarding interface.
Select the BYOL Plan
-
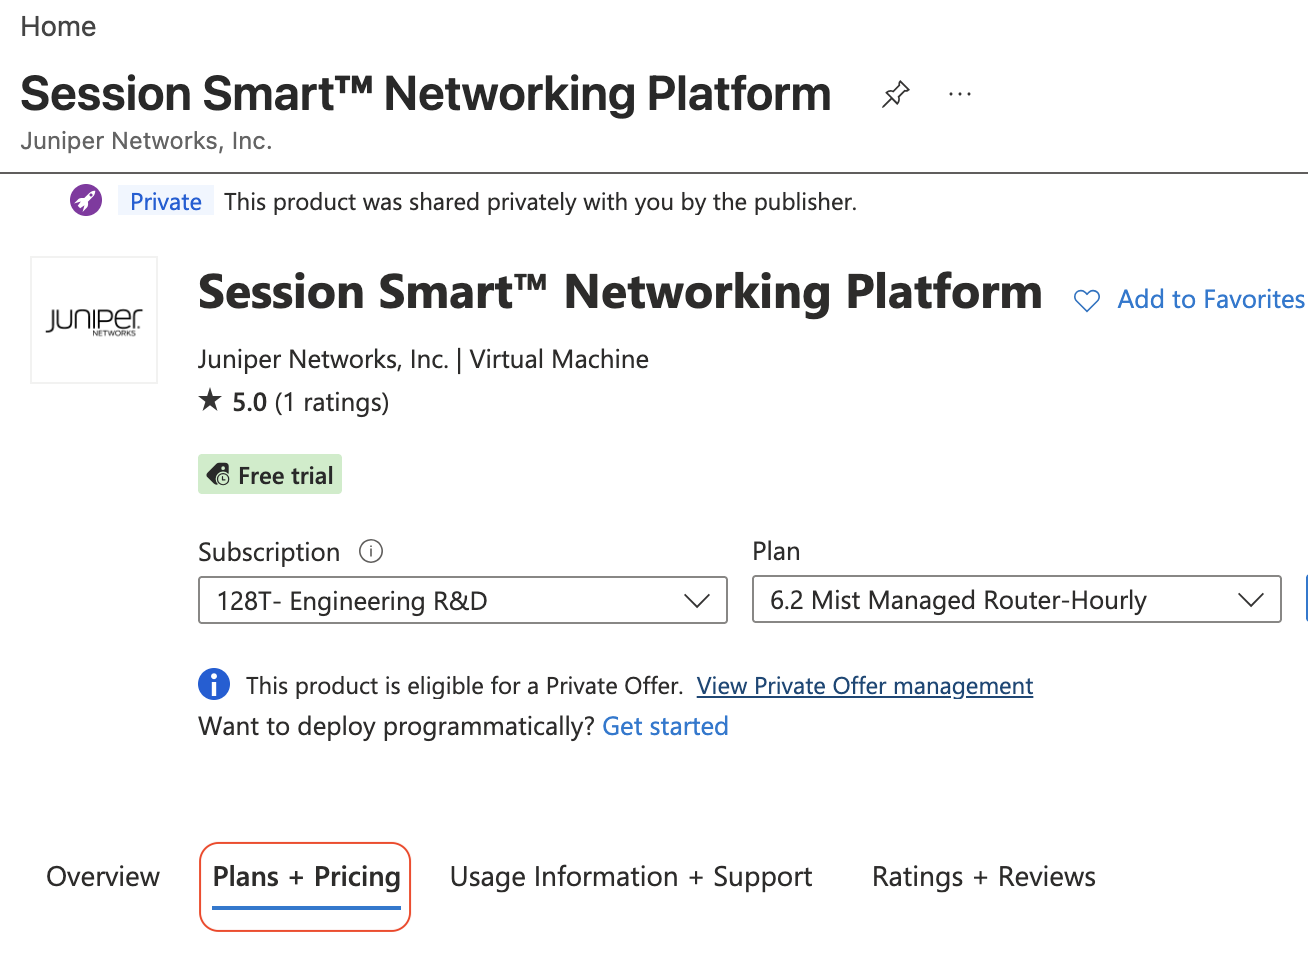
Go to the Session Smart Networking Platform in the Azure Marketplace.
-
Select the Plans + Pricing tab.
-
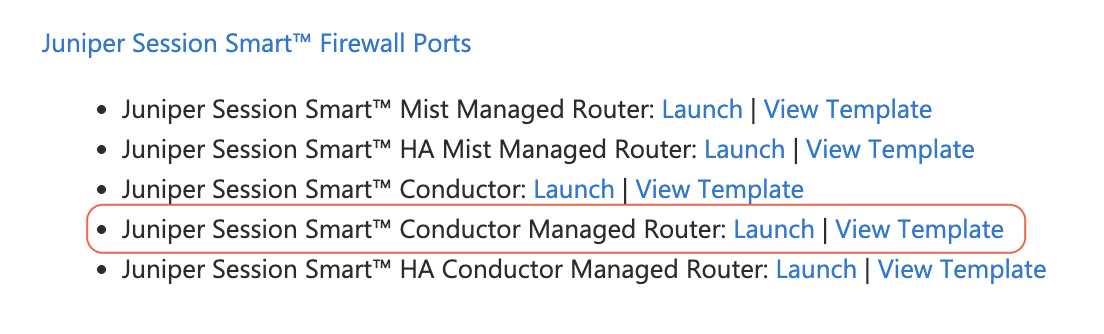
Scroll down to the bottom of the BYOL section.
-
Next to Juniper Session Smart Conductor-managed Router, click Launch.
Deploy via Azure Portal
-
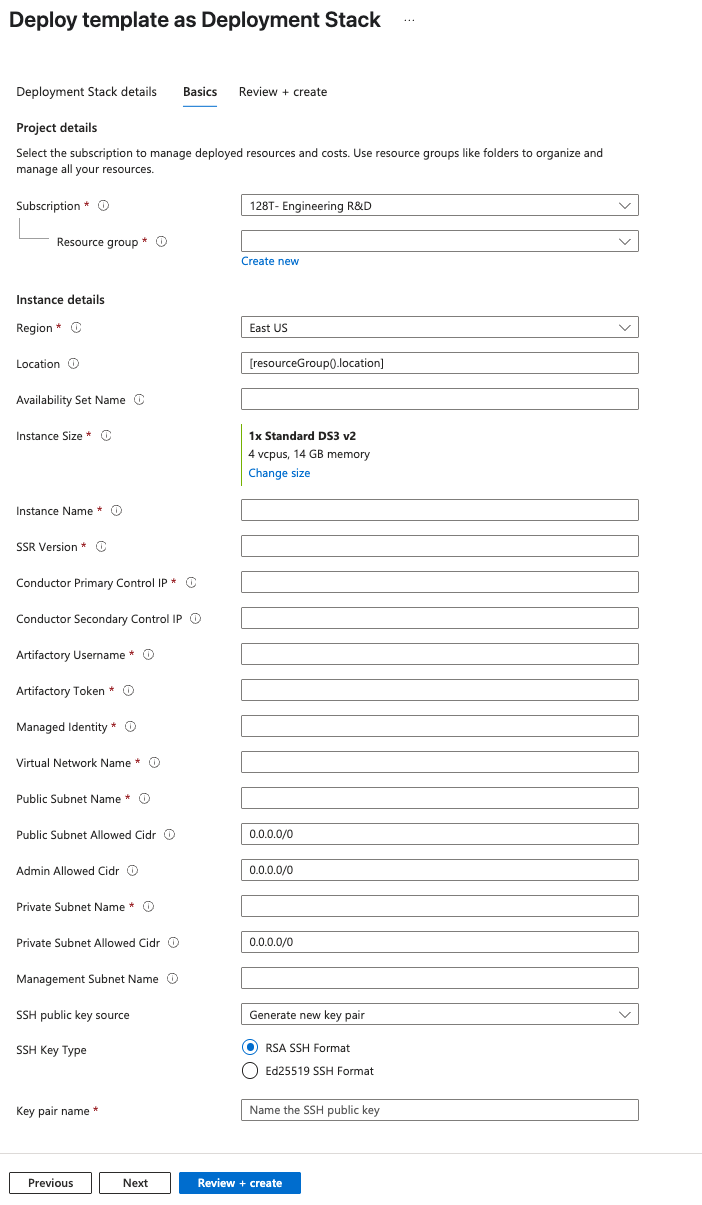
Fill in the template parameters using the following table.
Parameter Example Value Notes Subscription (your subscription) Subscription for the deployment. Resource Group SSR-RGSelect an existing Resource Group. Region eastusThe Azure location where the VNet exists. One word, all lowercase (for example, eastus,westus,westeurope). See Azure locations.Instance Size Standard_F8s_v2The Azure VM size to use for the router. Instance Name azure-hub-routerDisplay name for the VM. SSR Version 7.1.4The BYOL version to install. Primary Control IP <conductor-public-ip>Public IP of the conductor. Secondary Control IP (leave blank) Only required for HA conductor deployments. Artifactory Username (your username) User portion of the Juniper access credentials. Artifactory Token (your token) Token portion of the Juniper access credentials. Managed Identity (your managed identity) Must have the permissions listed in Requirements Virtual Network Name SSR-VNetSelect an existing VNet name. Public Subnet Name ssr-hub-wanHub WAN subnet. Public Subnet Allowed CIDR 0.0.0.0/0If the value is known at deployment time, it should be restricted.Source IP address range of the routers to be allowed for SVR traffic. Admin Allowed CIDR CIDR range allowed for SSH/HTTPS. This should be restricted at deployment time. Ingress rule allows SSH and HTTPs access from this IP address range. Private Subnet Name ssr-hub-lanHub LAN subnet. Private Subnet Allowed CIDR 0.0.0.0/0If the value is known at deployment time, it should be restricted.Source IP address range of the internal workloads to allow access. Admin Public Key Data (contents of your SSH public key) If you have an existing public key, select the appropriate response and provide the key. If not, generate a new one the first time, and reuse the same key subsequent times. cautionPublic Subnet Allowed CIDRandAdmin Allowed CIDRdefault to0.0.0.0/0for initial deployment. After the deployment completes and your environment is stable, update the associated NSG rules to restrict access forPublic Subnet Allowed CIDRto known source addresses. -
Click Next. Azure will validate the input.
-
After reviewing the Terms, click Create.
-
When the deployment completes, open the Outputs tab.
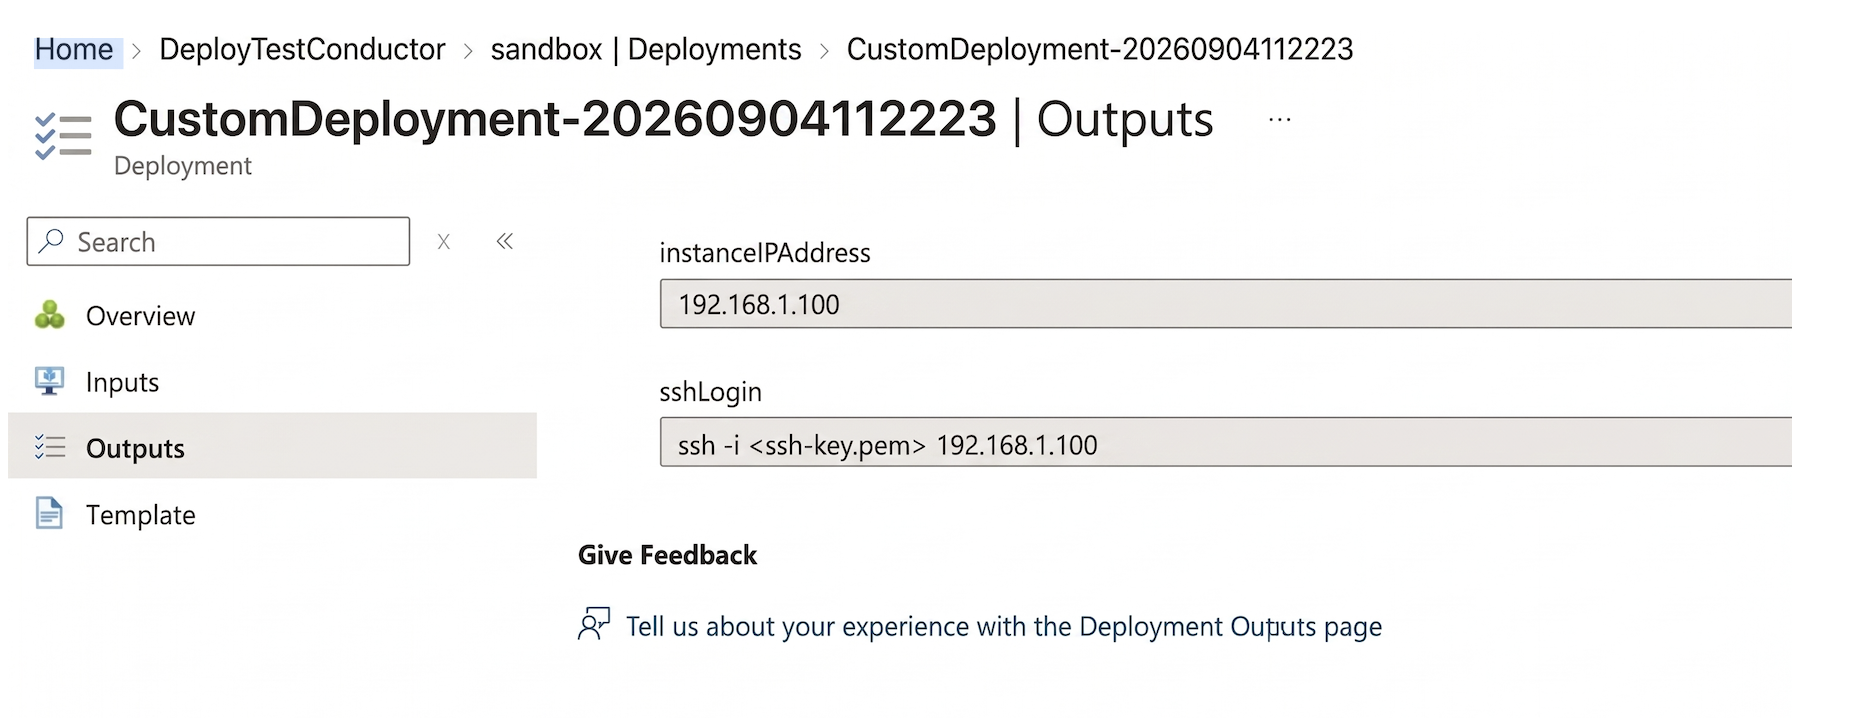
Make a note of the following value — you will need them in later steps:
- Public IP address: The router's Azure assigned public IP.
Network Interface Layout
Use the following interface information to assign the LAN and WAN interfaces later in this process.
| Linux Interface | Azure NIC Name | Subnet |
|---|---|---|
| ge-0-0 | azure-hub-router-public | ssr-hub-wan |
| ge-0-1 | azure-hub-router-private | ssr-hub-lan |
Next Step
Proceed to Step 2 — Create the Spoke Router VM.